Hashtag
#ActivityPub
15 posts tagged with this hashtag.
Security Update: Hollo 0.6.19 Released
We have released Hollo 0.6.19 to address a security vulnerability in Fedify's HTML parsing code.
This vulnerability (CVE-2025-68475) is a ReDoS (Regular Expression Denial of Service) issue that could allow an attacker to cause service unavailability by sending specially crafted HTML responses during federation operations. The malicious payload is small (approximately 170 bytes) but can block the Node.js event loop for extended periods.
We strongly recommend all Hollo operators upgrade to version 0.6.19 immediately.
| Field | Details |
|---|---|
| CVE | CVE-2025-68475 |
| Severity | High (CVSS 7.5) |
| Action | Upgrade to Hollo 0.6.19 |
github.com
ReDoS Vulnerability in HTML Parsing Regex
Hi Fedify team! 👋 Thank you for your work on Fedify—it's a fantastic library for building federated applications. While reviewing the codebase, I discovered a Regular Expression Denial of Servic...
A reminder to #ActivityPub developers and advocates: applications for the NLNet Open Social Fund close on June 1st (#BrookeVibberDay) at noon CEST. You should apply; you are doing important work and we need you to keep doing it.
nlnet.nl
NLnet; Open Social Fund
Hi #fediverse and #ActivityPub developers!
I'm currently working on interoperability testing for #Hollo and #Fedify, and I need a #Bonfire account to test federation with their implementation.
Since there aren't many open public Bonfire instances available, I was wondering if any Bonfire instance admins out there would be willing to grant me a test account? It would be a huge help for improving interop! Let me know if you can help. Thanks!

Should I try another ActivityPub platform? I shouldn't, right?
- Do it2 (100%)
- No one needs that much activity in their pub0 (0%)
A reminder to #ActivityPub developers and advocates: applications for the NLNet Open Social Fund close on June 1st (#BrookeVibberDay) at noon CEST. You should apply; you are doing important work and we need you to keep doing it.
nlnet.nl
NLnet; Open Social Fund
Hollo 0.9.0 is out. https://github.com/fedify-dev/hollo/discussions/496
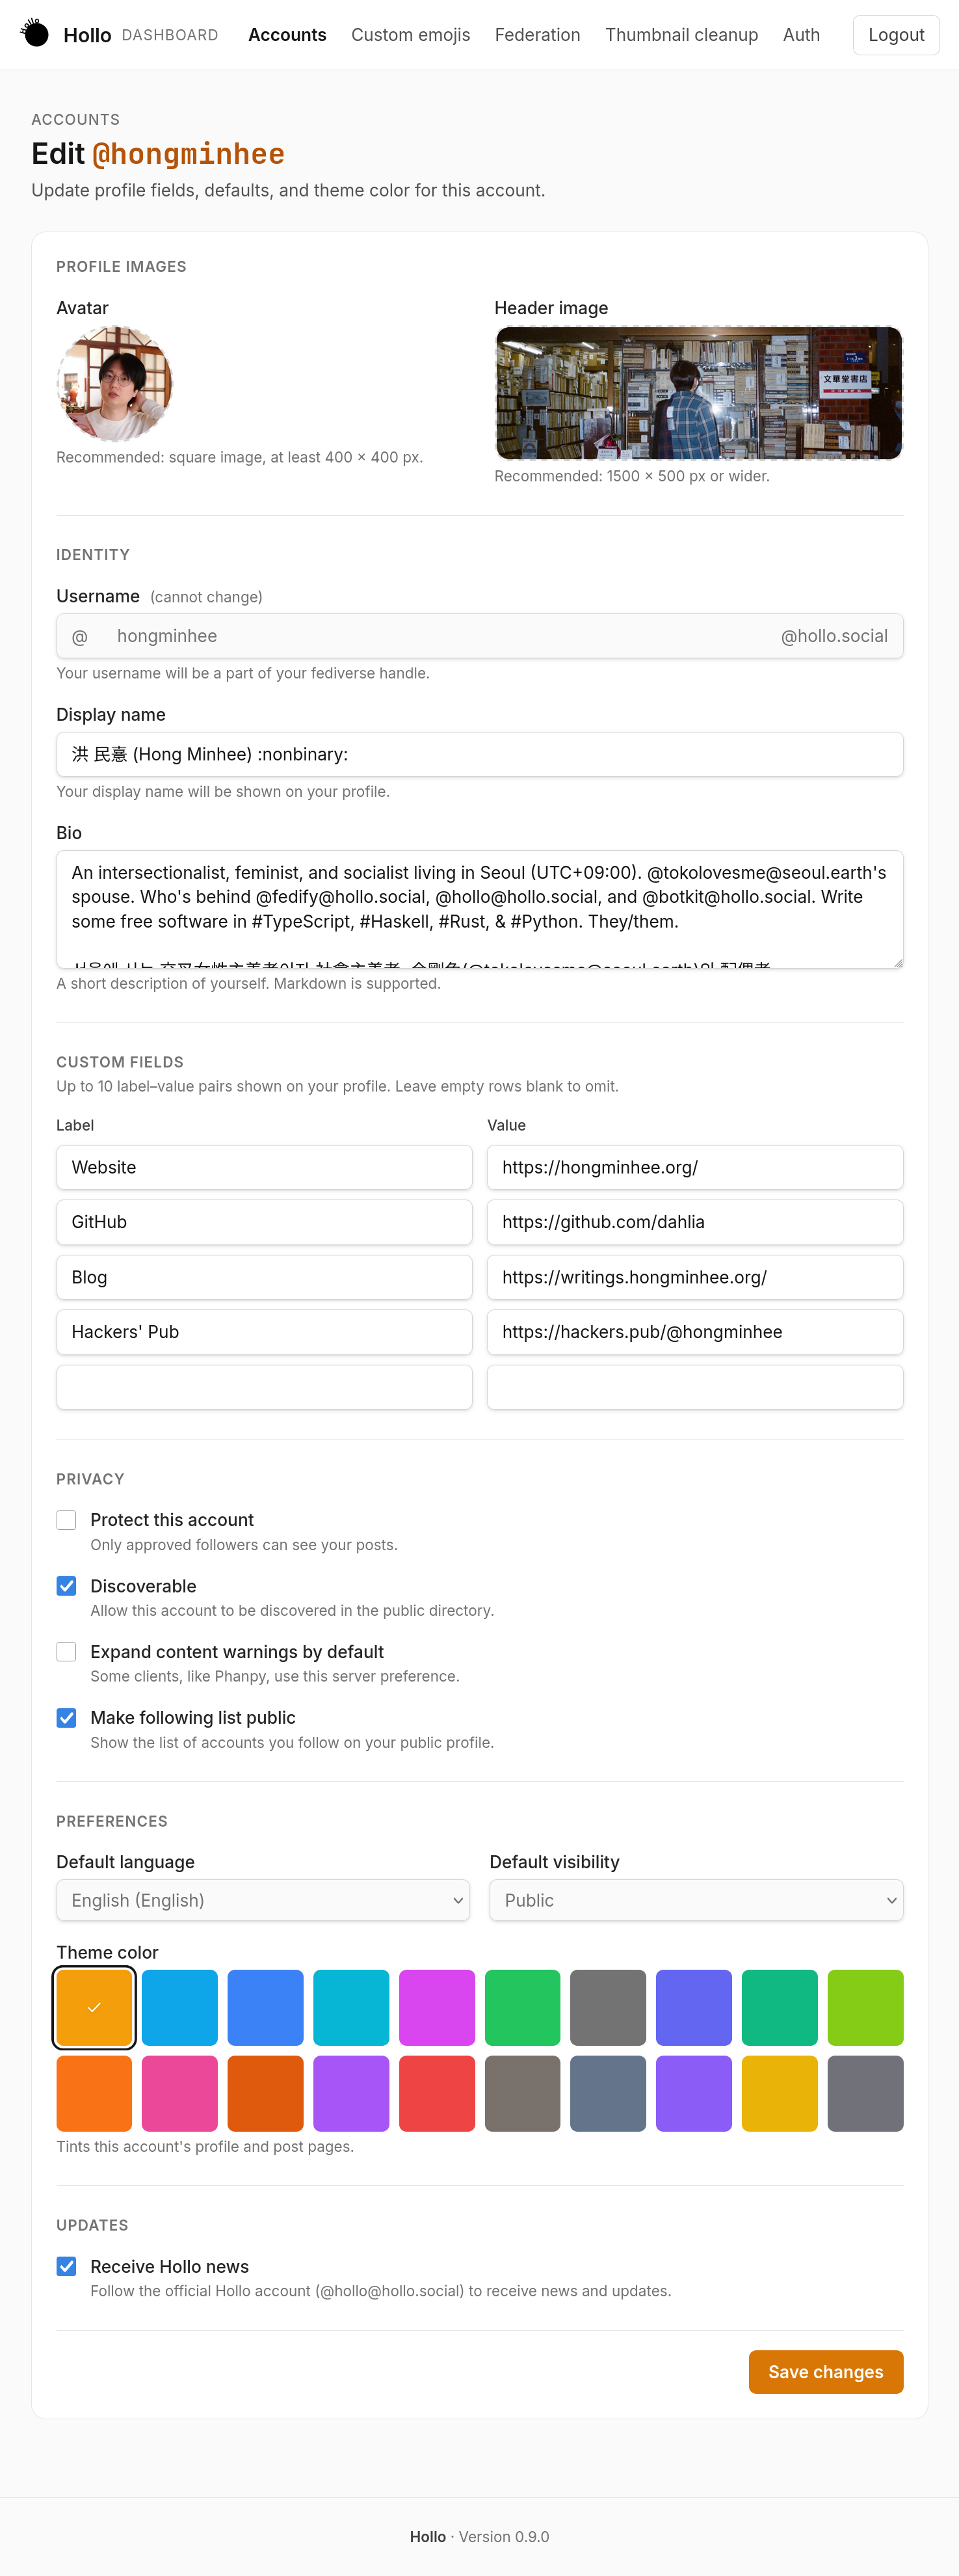
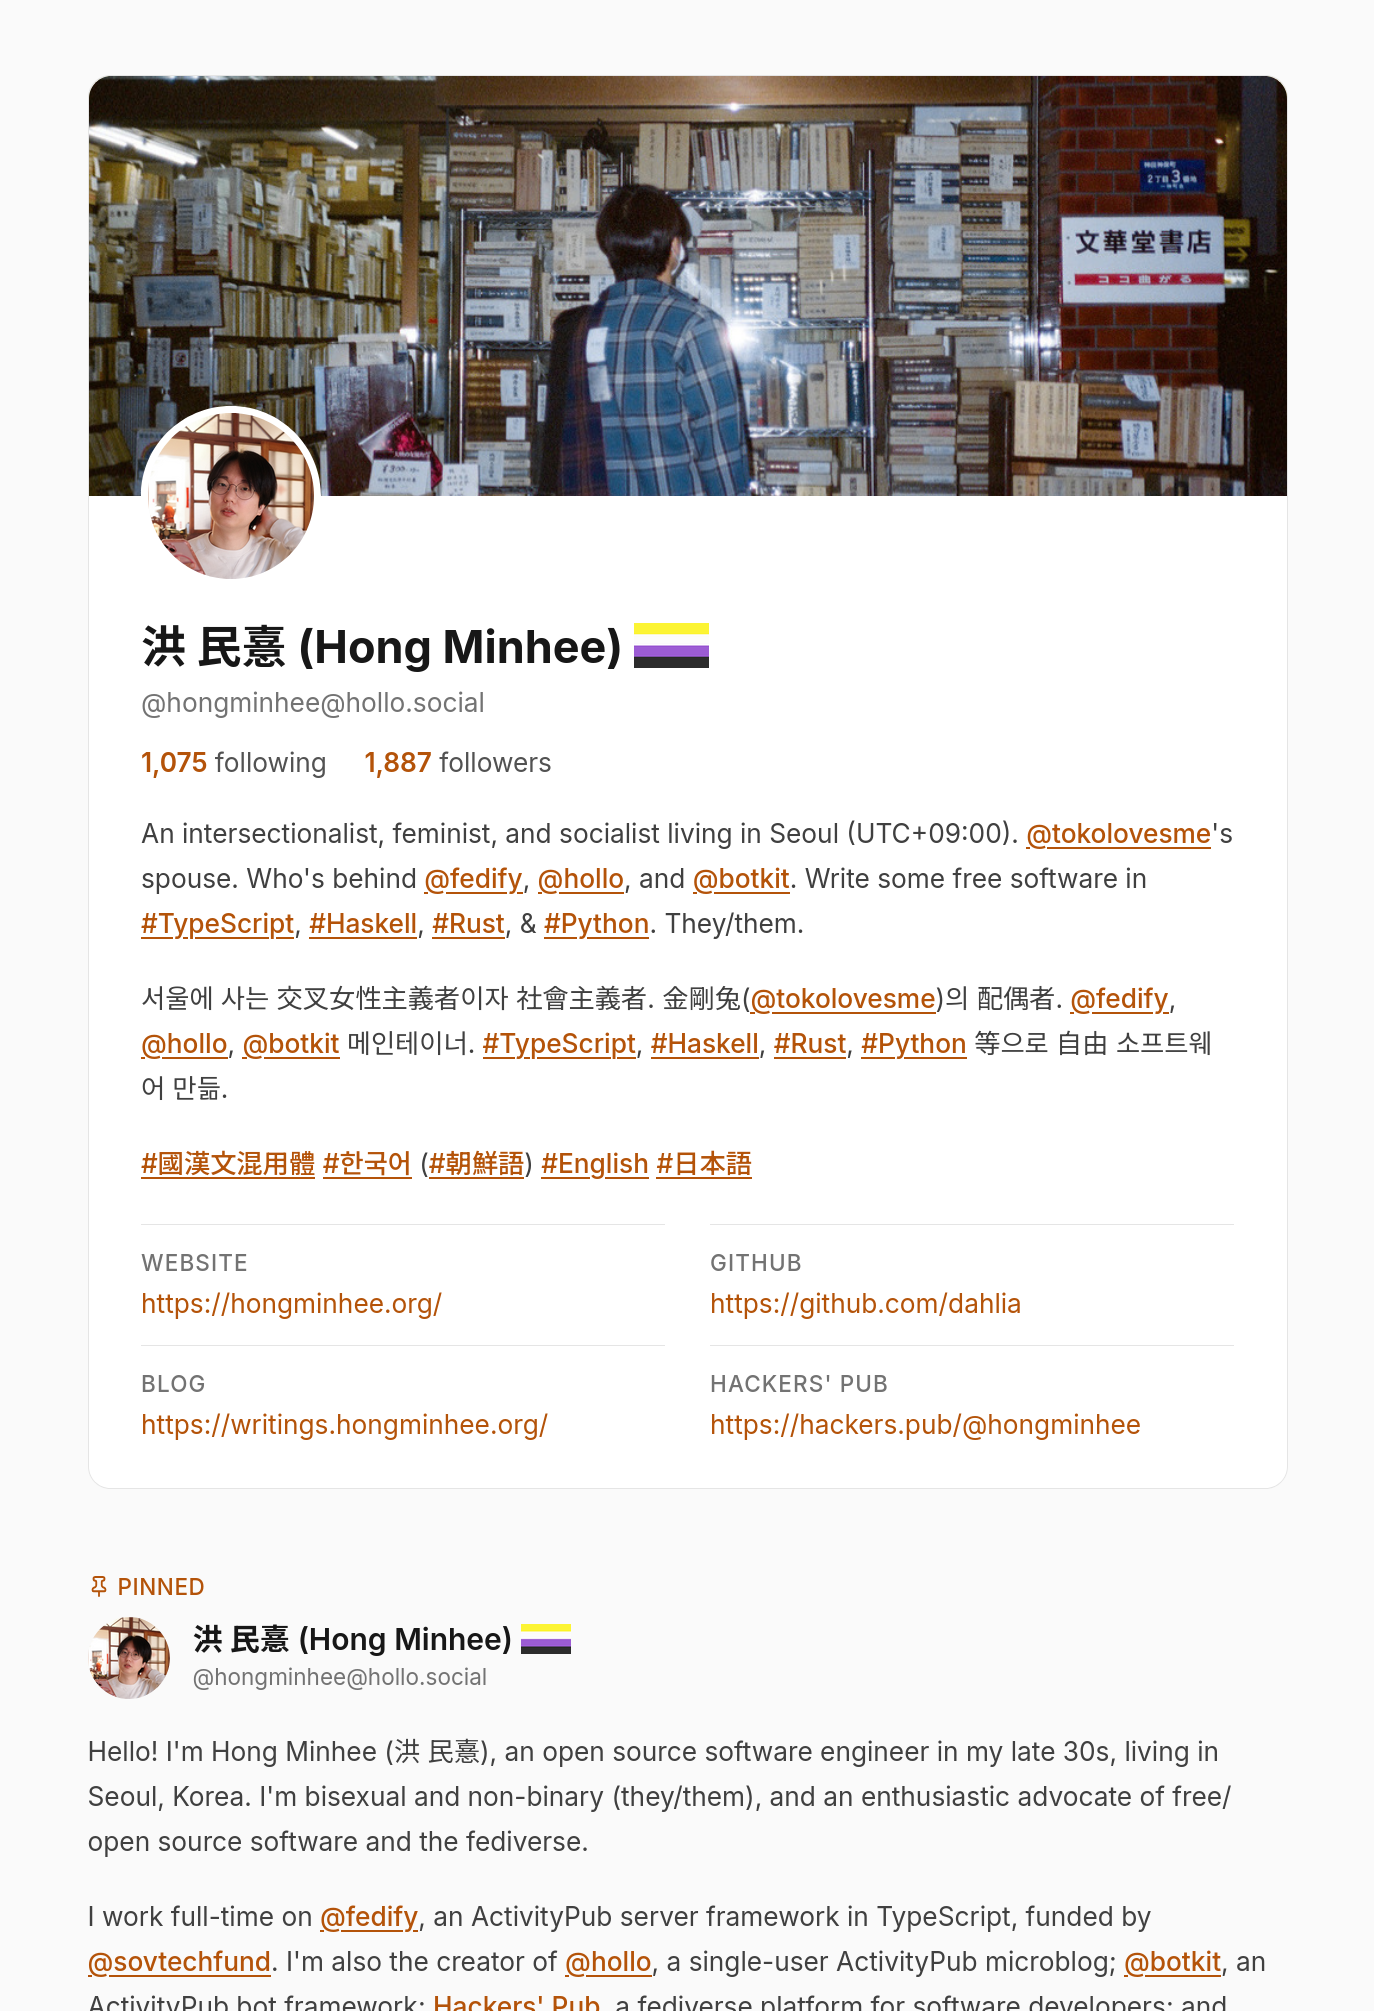
The biggest change this release is a complete redesign of every server-rendered page. Pico CSS is replaced by a new design system built on UnoCSS, and your chosen theme color now tints your profile and dashboard pages throughout.
Other highlights:
- Passkey (WebAuthn) authentication: sign in with a biometric or PIN gesture, which counts as MFA so there's no separate TOTP step
- Full FEP-044f quote authorization:
QuoteRequest/Accept/Rejectfederation, quote policy enforcement, and dereferenceableQuoteAuthorizationobjects - A configurable media proxy (
MEDIA_PROXY=proxyorcache) that re-serves remote avatars, attachments, and preview images from Hollo's own origin - Optional split-domain WebFinger via
HANDLE_HOST+WEB_ORIGIN - Public followers/following pages and per-post reaction list pages (likes, boosts, emoji reactions, quotes)
There were also several serious database performance fixes: profile page queries that were taking hundreds of seconds on cold caches, a NodeInfo endpoint doing a full table scan on every request, and a handful of timeline pagination bugs.
ALT text
The “Edit @hongminhee” admin page showing the new Hollo design: profile image upload areas for avatar and header, identity fields for display name and bio, custom fields table with label-value pairs, privacy checkboxes, a 20-swatch theme color picker with orange selected, and a “Save changes” button
ALT text
Public profile for 洪 民憙 (Hong Minhee) with a bookstore header image, circular avatar, follower and following counts, bio, custom fields including website and GitHub links, and a pinned post card below
Hi #fediverse and #ActivityPub developers!
I'm currently working on interoperability testing for #Hollo and #Fedify, and I need a #Bonfire account to test federation with their implementation.
Since there aren't many open public Bonfire instances available, I was wondering if any Bonfire instance admins out there would be willing to grant me a test account? It would be a huge help for improving interop! Let me know if you can help. Thanks!
We talk about #HolosSocial forgetting some of you might not know this project.
#Holos is a full ActivityPub server running on your device. Currently on Android, next on iOS.
We already introduced #E2EE DMs and #ActivityPub identity through custom domains. You own your followers, your keys, and your identity. Relays are just infrastructure.
On the footer of https://holos.social we added pages explaining the project. Have a look!
Mastodon: @HolosSocial Don't hesitate to share
holos.social
Fediverse Relay - Your Device is Your Fediverse Server
Your device is your fediverse server. End-to-end encrypted DMs, multi-device sync, custom domains. Powered by ActivityPub.
@[email protected] · Reply to Hollo :hollo:
セキュリティアップデート: Hollo 0.6.19 リリース
FedifyのHTMLパースコードにおけるセキュリティ脆弱性に対応したHollo 0.6.19をリリースしました。
この脆弱性 (CVE-2025-68475) は ReDoS (正規表現によるサービス拒否) の問題であり、攻撃者がフェデレーション操作中に特別に細工されたHTMLレスポンスを送信することで、サービス停止を引き起こす可能性があります。悪意のあるペイロードは小さい (約170バイト) ですが、Node.jsのイベントループを長時間ブロックする可能性があります。
すべてのHollo運営者の皆様には、直ちにバージョン 0.6.19 へのアップグレードを強くお勧めします。
| 項目 | 詳細 |
|---|---|
| CVE | CVE-2025-68475 |
| 深刻度 | 高 (CVSS 7.5) |
| 対応 | Hollo 0.6.19 にアップグレード |
github.com
ReDoS Vulnerability in HTML Parsing Regex
Hi Fedify team! 👋 Thank you for your work on Fedify—it's a fantastic library for building federated applications. While reviewing the codebase, I discovered a Regular Expression Denial of Servic...
@[email protected] · Reply to Hollo :hollo:
보안 업데이트: Hollo 0.6.19 릴리스
Fedify의 HTML 파싱 코드에서 발견된 보안 취약점을 수정한 Hollo 0.6.19를 릴리스했습니다.
이 취약점(CVE-2025-68475)은 ReDoS(정규 표현식 서비스 거부) 문제로, 공격자가 연합 작업 중 특수하게 조작된 HTML 응답을 보내 서비스 장애를 유발할 수 있습니다. 악성 페이로드는 작지만(약 170바이트), Node.js 이벤트 루프를 장시간 차단할 수 있습니다.
모든 Hollo 운영자분들께 즉시 버전 0.6.19로 업그레이드하실 것을 강력히 권고드립니다.
| 항목 | 상세 |
|---|---|
| CVE | CVE-2025-68475 |
| 심각도 | 높음 (CVSS 7.5) |
| 조치 | Hollo 0.6.19로 업그레이드 |
github.com
ReDoS Vulnerability in HTML Parsing Regex
Hi Fedify team! 👋 Thank you for your work on Fedify—it's a fantastic library for building federated applications. While reviewing the codebase, I discovered a Regular Expression Denial of Servic...
Security Update: Hollo 0.6.19 Released
We have released Hollo 0.6.19 to address a security vulnerability in Fedify's HTML parsing code.
This vulnerability (CVE-2025-68475) is a ReDoS (Regular Expression Denial of Service) issue that could allow an attacker to cause service unavailability by sending specially crafted HTML responses during federation operations. The malicious payload is small (approximately 170 bytes) but can block the Node.js event loop for extended periods.
We strongly recommend all Hollo operators upgrade to version 0.6.19 immediately.
| Field | Details |
|---|---|
| CVE | CVE-2025-68475 |
| Severity | High (CVSS 7.5) |
| Action | Upgrade to Hollo 0.6.19 |
github.com
ReDoS Vulnerability in HTML Parsing Regex
Hi Fedify team! 👋 Thank you for your work on Fedify—it's a fantastic library for building federated applications. While reviewing the codebase, I discovered a Regular Expression Denial of Servic...
 Introducing #BotKit: A #TypeScript framework for creating truly standalone #ActivityPub bots!
Unlike traditional Mastodon bots, BotKit lets you build fully independent #fediverse bots that aren't constrained by platform limits. Create your entire bot in a single TypeScript file using our simple, expressive API.
Currently #Deno-only, with Node.js & Bun support planned. Built on the robust @fedify foundation.
botkit.fedify.dev
Standalone ActivityPub bots in TypeScript
BotKit is a TypeScript framework for building standalone ActivityPub bots for the fediverse: its own server, not a Mastodon or Misskey account. Built by the Fedify team.

Fedify is an #ActivityPub server framework in #TypeScript & #JavaScript. It aims to eliminate the complexity and redundant boilerplate code when building a federated server app, so that you can focus on your business logic and user experience.
The key features it provides currently are:
- Type-safe objects for Activity Vocabulary (including some vendor-specific extensions)
- #WebFinger client and server
- HTTP Signatures & Linked Data Signatures & Object Integrity Proofs
- Middleware for handling webhooks
- #NodeInfo protocol
- #Node.js, #Deno, and #Bun support
- CLI toolchain for testing and debugging
If you're curious, take a look at the #Fedify website! There's comprehensive docs, a demo, a tutorial, example code, and more:

fedify.dev
Fedify
Fedify is a TypeScript library for building federated server apps powered by ActivityPub and other standards, so-called fediverse.
Introducing #Hollo. Hollo is an #ActivityPub-enabled single-user microblogging software. Although it's for a single user, it also supports creating and running multiple accounts for different topics.
It's headless, meaning you can use existing #Mastodon client apps instead, with its Mastodon-compatible APIs. It has most feature parity with Mastodon. Two big differences with Mastodon is that you can use #Markdown in the content of your posts and you can quote another post.
Oh, and Hollo is built using #Bun and #Fedify.